Community post
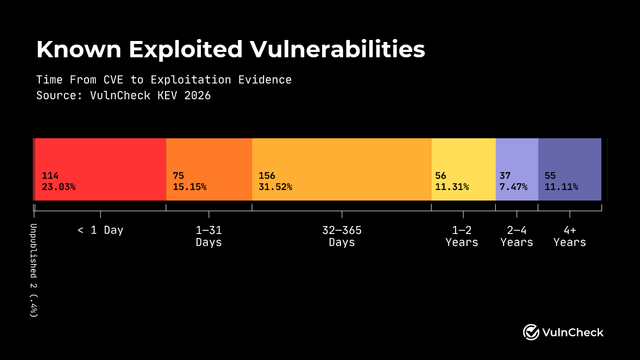
Just the rumour of a bug is enough to find an exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond Source: recoil.org (251 points, 89 comments) Hacker News discussion


